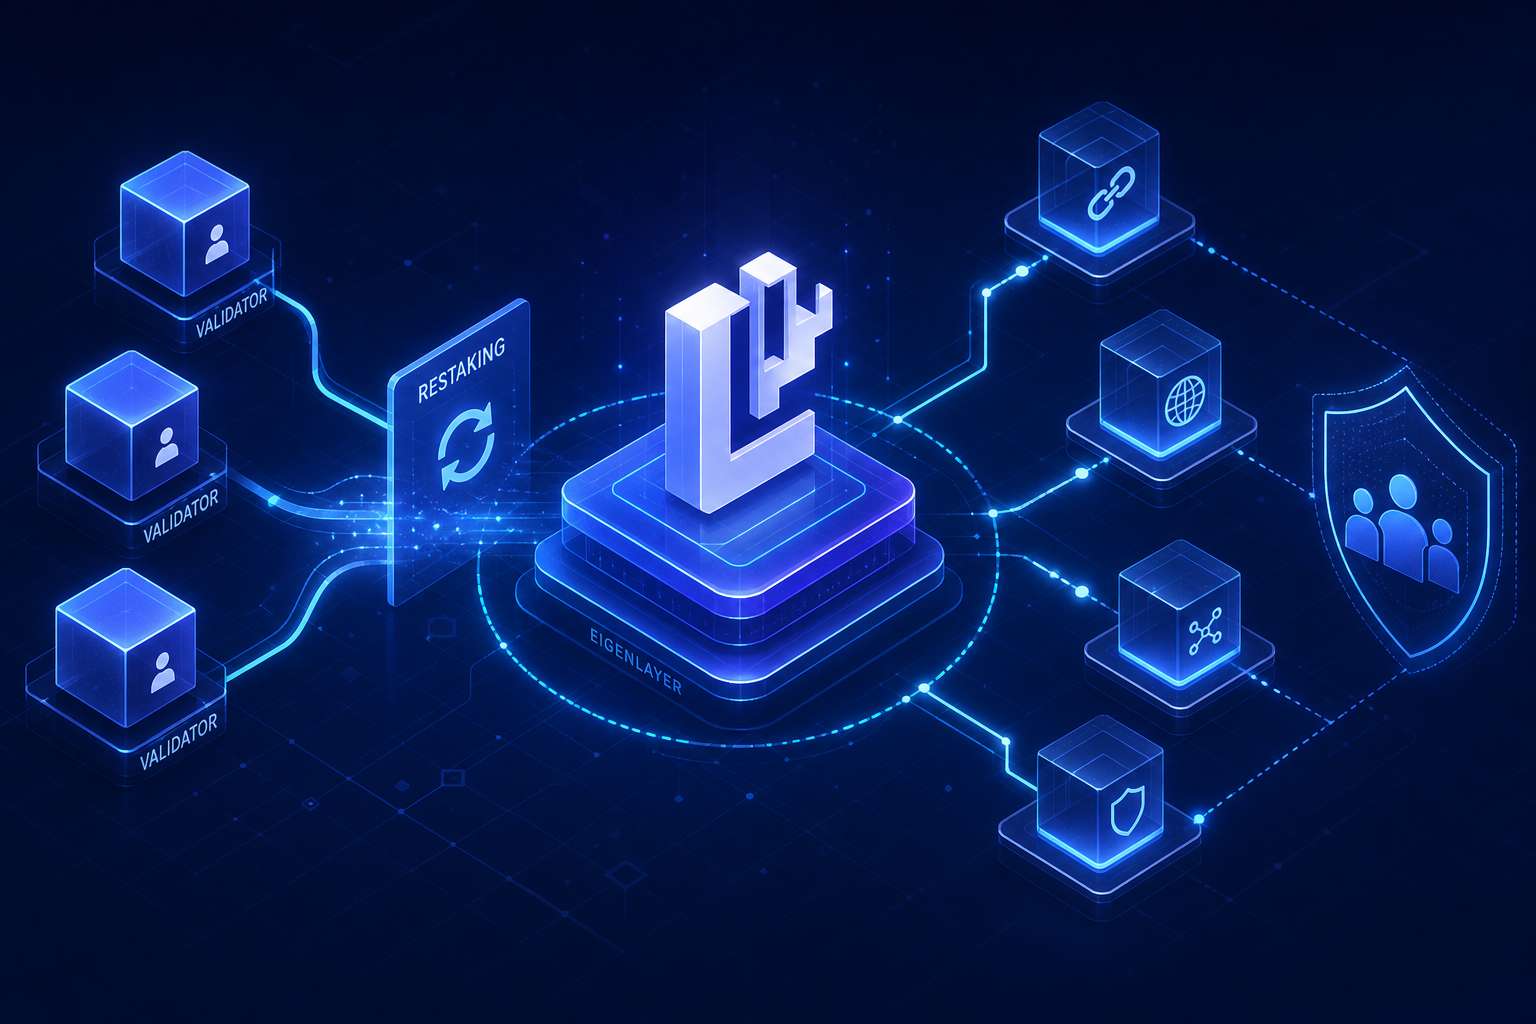
Restaking: EigenLayer and Shared Security
Restaking means using ETH or liquid staking assets you have already staked to provide additional economic security to other decentralized services, and earning extra rewards for doing so. EigenLayer is one of the representative protocols for this mechanism, and its core idea is to let Ethereum's existing staked capital provide "shared security" to other services, on the condition that it takes on additional risk.
In simple terms:
Regular staking: ETH → secures Ethereum → you earn staking rewards
Restaking: ETH/LST → secures Ethereum + other services → you earn base staking rewards + extra rewards
But this does not mean "the same ETH can earn two risk-free yields." The more security responsibilities an asset carries, the more potential penalties and protocol risks it takes on.
What is Restaking?
Restaking can be understood as "reusing" assets that have already been staked.
In a PoS network, the main role of staked ETH is to participate in consensus and keep the network secure. Restaking goes further by allowing these assets, which already carry economic security responsibilities, to provide security guarantees for other protocols, applications, or infrastructure.
Ethereum's official definition of restaking is: using already-staked ETH to secure other decentralized services and earn additional rewards. These protected services are usually called AVSs (Actively Validated Services).
So the core of restaking is not simply "depositing the same token twice," but rather:
Extending an existing pool of economic security so that more services can use it.
Why is shared security needed?
If a new project wants to build a decentralized service, it usually has to answer a very practical question:
Who secures this system?
The traditional approach is for the project to issue its own token, have users stake that token, and build economic security for its own network or service that way.
But for a protocol that has just launched, this creates a cold-start problem:
It needs a large amount of capital first;
It needs to attract validators;
It needs to build enough economic security;
It needs to make attackers believe that attacking costs more than it pays.
If security capital is insufficient, a highly valuable service can become an attack target.
Restaking offers another approach:
Instead of making every new service build a security budget from scratch, let them use ETH staking capital that already exists.
EigenLayer's design philosophy is exactly this: to build a shared security marketplace where validators can choose which modules or services to provide extra security for, and those services can tap into staking capital that already exists.
What is EigenLayer?
EigenLayer is one of the most representative restaking protocols in the Ethereum ecosystem.
Its core is not to create another independent blockchain, but to build a mechanism on top of Ethereum that lets ETH stakers choose to use their staked capital to secure other services.
Within the EigenLayer system, these services are called AVSs.
You can think of EigenLayer as a marketplace connecting three parties:
Stakers ↔ Operators ↔ AVSs (Actively Validated Services)
Stakers supply economic security, operators run the relevant software and perform validation tasks, and AVSs receive security backed by that staked capital. In exchange, the participants involved can earn rewards offered by the protocol or the service.
This is also the heart of the "shared security" concept.
What is an AVS?
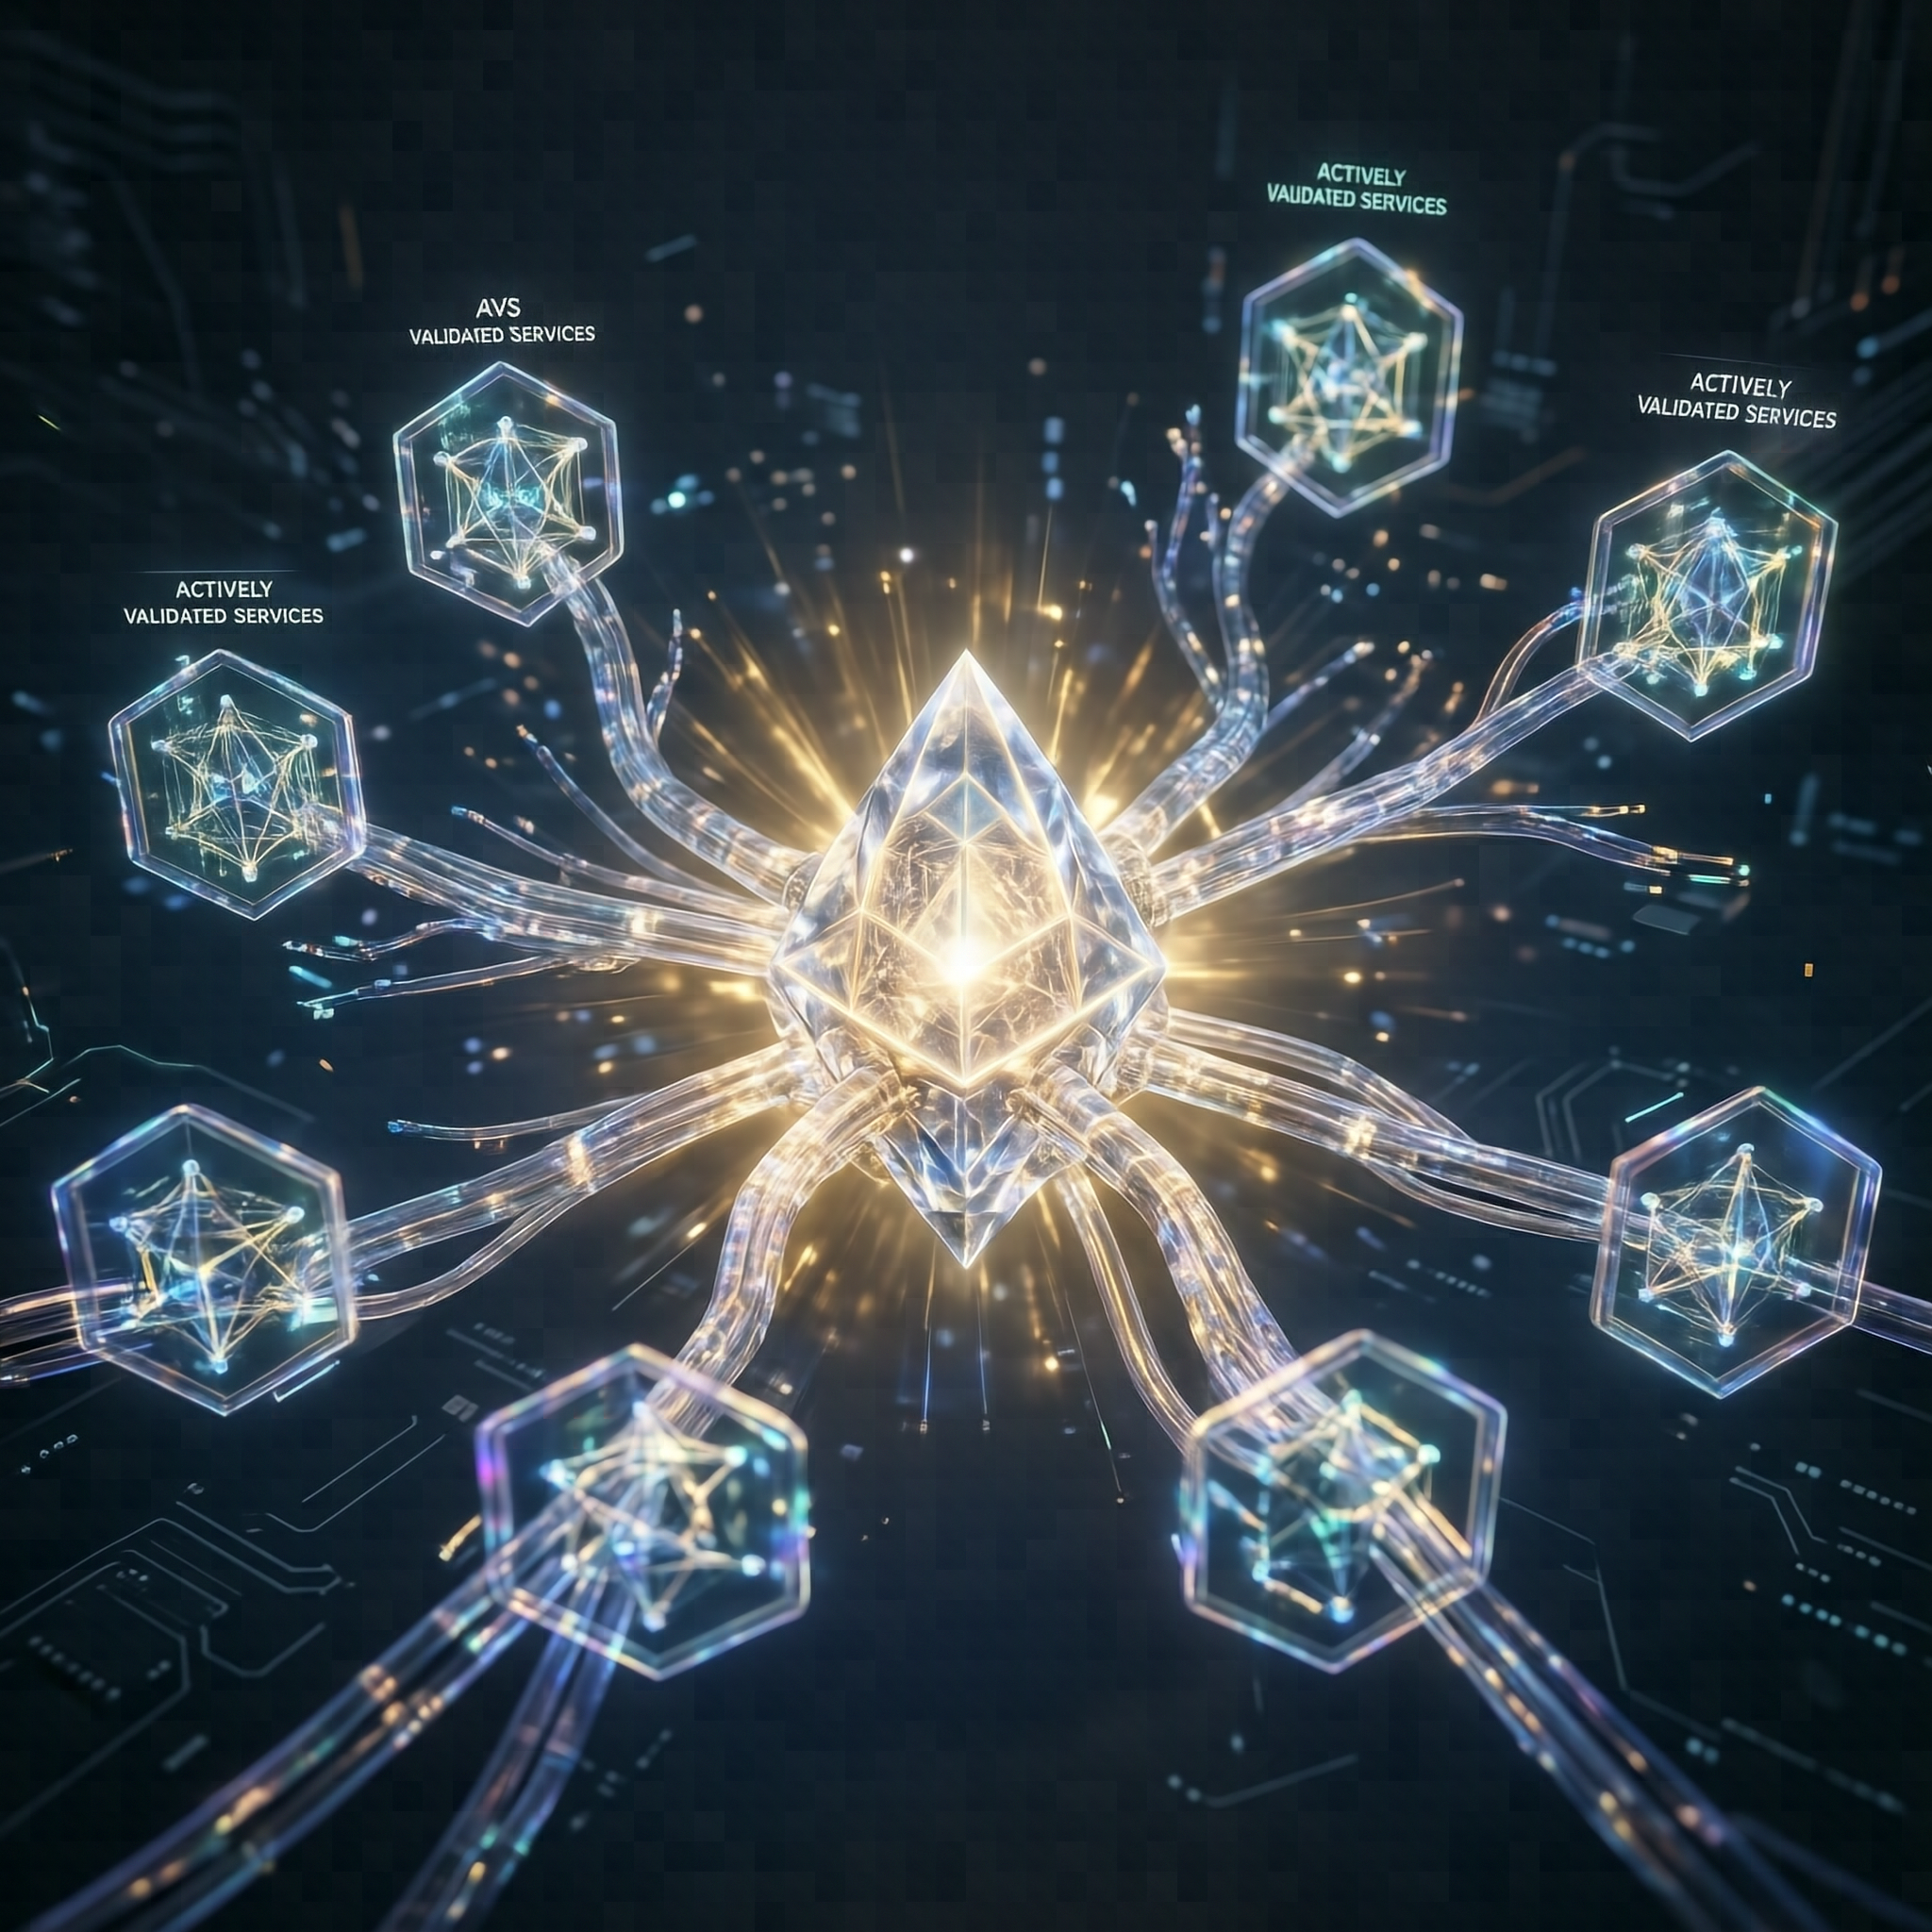
AVS stands for Actively Validated Services, which you can think of as decentralized services that need an additional layer of validation and economic security.
These services are not necessarily Layer 1 blockchains in the traditional sense; they can also be other kinds of infrastructure.
Examples currently listed by Ethereum's official documentation include:
Oracles;
Cross-chain bridges;
Data systems;
Other services that need decentralized validation.
Why do these services need security?
Because if an oracle feeds in wrong data, a bridge system is attacked, or a data service is maliciously manipulated, the applications and assets built on top of them can ultimately be affected.
The goal of restaking is to let these services obtain an extra layer of economic security by drawing on staking capital that already exists.
How does a typical EigenLayer flow work?
A typical restaking process can be broken down into several steps.
Step 1: The user holds already-staked ETH
Users can run an Ethereum validator themselves, or obtain an LST through liquid staking.
If you are not yet familiar with LSTs, you can start with Liquid Staking (LSD/LRT): Making Your Staked Assets Liquid.
Step 2: The user chooses to take part in restaking
The user connects eligible staked assets to the restaking system and, following the rules, chooses which services to support.
The key point here is that it is not "automatically securing every AVS": users, or the operators they delegate to, need to choose which services to participate in based on the specific mechanism.
Step 3: The operator performs validation tasks
An operator can be understood as a professional participant responsible for running the relevant software and infrastructure.
Ethereum's official materials show that operators run the software an AVS requires and perform the corresponding validation tasks. Stakers can delegate their assets to an operator, so they do not have to maintain the extra software that every AVS requires themselves.
Step 4: The AVS obtains shared security
The AVS uses the economic security provided by these participants to run its own service.
Compared with building a full security system from scratch, it can draw on ETH staking capital that already exists.
Step 5: Participants earn extra rewards
If the AVS or the related protocol offers rewards, participants can earn additional income on top of their existing ETH staking yield.
But one thing must be emphasized here:
Extra rewards correspond to extra security responsibilities.
If the AVSs you participate in have additional penalty conditions, the related staked assets may also face additional risk.
What is the difference between Native Restaking and LST Restaking?
Restaking is not limited to a single way of participating.
Native Restaking
Native restaking is usually suited to users who run an Ethereum validator themselves.
Users restake the ETH they have already staked directly and, following the relevant mechanism, choose which AVSs to support.
This approach demands more technical skill and infrastructure.
LST Restaking
If users do not run a validator themselves, they can obtain an LST through liquid staking and then restake eligible LSTs.
For example:
ETH → Liquid Staking → LST → Restaking
This approach lowers the barrier to entry, but users also take on the LST's own protocol, liquidity, and depeg risks.
So LST restaking is not simply "click one more button and earn one more layer of yield"; it adds another layer of protocol relationships on top of the existing asset structure.
What is the difference between restaking and regular staking?
The most fundamental difference is what the security is protecting.
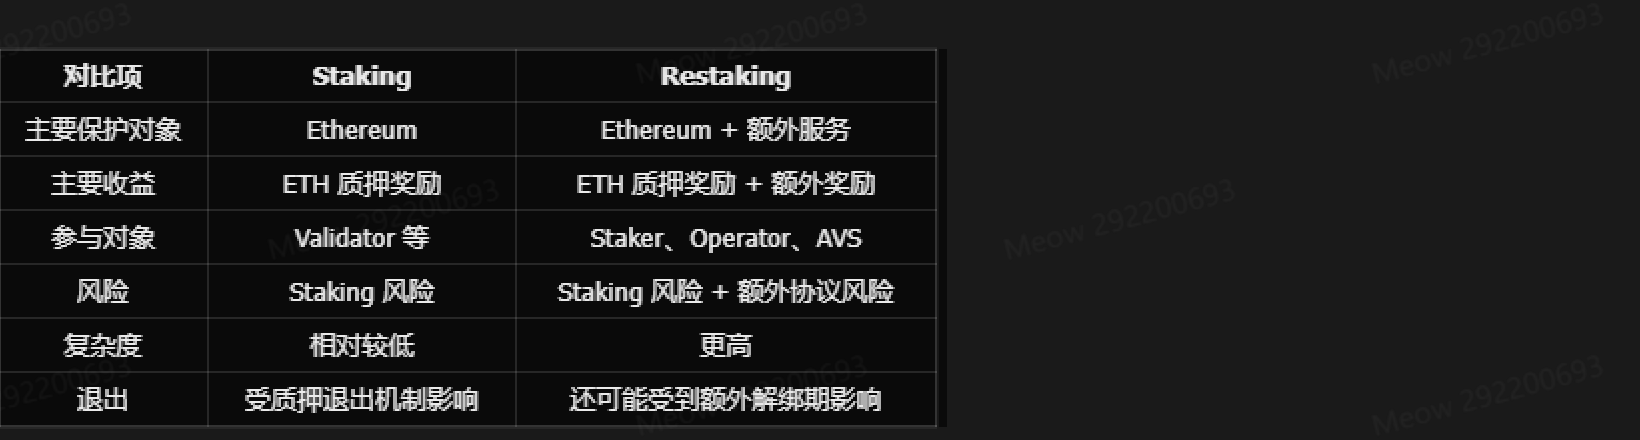
Ethereum's official documentation also makes clear that restaking carries a broader risk surface than regular staking, and that withdrawals may involve additional unbonding time beyond the base exit queue.
So if someone tells you:
"Restaking just doubles your staking yield."
That statement is not accurate.
A more accurate understanding is:
Restaking extends the security responsibilities of staked capital to more services, so it may earn extra rewards while also taking on extra risk.
Where do restaking rewards come from?
Restaking rewards do not usually appear out of nowhere.
The most basic layer is still:
Ethereum Staking Rewards
On top of that, participating in additional services may earn you:
AVS / service rewards
So the theoretical sources of return can be understood as:
Base staking yield + restaking rewards − fees − potential losses
But the specific reward mechanisms of different protocols and services can be completely different.
So when you see an LRT or restaking product showing a high APY, the first thing you should do is not compare the numbers, but ask:
Who is actually paying the extra yield?
If the yield comes from some kind of token incentive, you also need to judge the token's own liquidity, price volatility, and how long the incentive will last.
Why can't restaking rewards simply be added together?
Suppose an ETH staking strategy provides a base yield, and restaking shows an additional yield.
On the surface:
Base yield + restaking yield = higher APY
But risk can increase at the same time.
Suppose the same asset participates in several services at once; then that asset effectively has to follow the rules of several systems.
If a participant misbehaves, the corresponding penalty mechanism may be triggered; and if multiple services share the same staked capital, in extreme cases a risk event for one participant can also affect several services that depend on that capital.
Ethereum's official documentation specifically points out that restaking carries Chain Reactions risk: if a restaker is slashed while securing multiple AVSs, the level of security the other AVSs rely on may fall further.
This is also one of the most important risk concepts to understand about restaking.
What is the biggest risk of restaking?
1. Extra slashing risk
This is one of the most important differences between restaking and regular staking.
Regular staking already has protocol penalty mechanisms, and restaking can add further penalty conditions on top.
EigenLayer's design documents state explicitly that participants who opt into different modules must accept the corresponding additional slashing conditions.
So:
Participating in more services does not necessarily mean earning more; it also means understanding more penalty rules.
2. Smart contract risk
Restaking usually relies on smart contracts to manage assets, delegation relationships, and service participation.
If those contracts have vulnerabilities, flawed permission design, or other security defects, funds can be lost.
And restaking often involves multiple protocols, so the risk surface can be more complex than plain staking.
3. Operator risk
If users delegate these responsibilities to an operator, they need to consider how well that operator performs.
For example:
Whether it runs reliably over the long term;
Whether it has sufficient infrastructure;
Whether there are centralization problems;
Whether it might misbehave.
An operator is not an intermediate layer that is completely free of risk.
4. AVS risk
The security of restaking ultimately also depends on the AVSs being protected.
If an AVS itself has design flaws, economic model problems, or validation mechanism vulnerabilities, stakers may take on extra risk for limited returns.
So you should not only study the "restaking platform," but also study exactly which AVSs you are providing security for.
5. Exit and liquidity risk
Restaked assets cannot necessarily be retrieved immediately.
Ethereum's official documentation currently states clearly that exiting restaked assets may be affected both by the base staking exit queue and by additional unbonding mechanisms.
So if users need to be able to access their funds at any time, they must check the exit rules of the specific product in advance.
6. The "over-reuse" risk of shared security
This is one of the most important systemic risks to understand about restaking.
Suppose the same pool of staked capital secures several AVSs at once:
AVS A ← same staked capital → AVS B ← same staked capital → AVS C
If something goes seriously wrong with that capital, the impact can spread to several services at the same time.
Ethereum's official documentation also lists this potential "Chain Reactions" effect as one of the risks of restaking.
So the advantage of shared security is that it improves capital efficiency, while its challenge is:
The same pool of security capital cannot be reused an unlimited number of times.
How does restaking relate to LRTs?
An LRT, or Liquid Restaking Token, can be understood as a tokenized form that keeps restaked assets at least somewhat liquid.
A simplified flow is:
ETH → Staking → LST → Restaking → LRT
Once users hold an LRT, they can keep using this kind of asset in the DeFi environments that specifically support it.
But an LRT does not remove restaking risk.
On the contrary, it can add further layers:
Underlying ETH risk + LST risk + restaking risk + LRT protocol risk
So the core value of an LRT is that it improves how composable your capital is, not that it makes risk disappear.
How do you judge whether a restaking project is worth joining?
You can use the framework below.
Step 1: Confirm the underlying asset
First work out what exactly you are staking.
Is it native ETH?
Or an LST such as stETH or rETH?
Different underlying assets mean different risks.
Step 2: Confirm what is being protected
Do not stop at "I am participating in restaking." You need to know:
Who exactly is my asset protecting?
Which specific AVS is it?
What does this AVS do?
Why does it need economic security?
Step 3: Confirm where the extra rewards come from
The key question is:
Who is paying the extra yield?
Is it an AVS service fee?
Is it a protocol token?
Or is it a temporary incentive program?
If the rewards mainly come from token incentives, you need to consider the price of the reward token and how long the incentive will last.
Step 4: Confirm the penalty mechanism
This is a step that deserves particular attention in restaking.
You need to confirm:
What behavior triggers a penalty;
Who decides whether a violation occurred;
Who carries out the penalty;
Whether stakers bear it;
Whether penalties for different AVSs are independent of one another.
Step 5: Confirm the exit rules
Check:
Whether there is an unbonding period;
Whether there is an exit queue;
Whether the LRT can be redeemed directly;
How liquid the secondary market is;
Whether you can exit normally in extreme market conditions.
Step 6: Do not look only at APY
What you should ultimately compare is:
Expected return − fees − potential risk cost
Rather than simply comparing:
Which product has the higher APY.
What kind of user is restaking suited to?
Restaking is better suited to users who already understand PoS staking, LSTs, and the basics of DeFi.
If users still do not understand validators, staking rewards, slashing, and LSTs, jumping straight into complex restaking strategies makes it very hard to judge what risks they are actually taking.
You can follow this order of learning:
Layer one: Staking
Start by understanding PoS and staking yield.
Layer two: LST
Understand why staked assets can be tokenized and made liquid again.
Layer three: Restaking
Understand how already-staked assets can provide security to other services.
Layer four: LRT
Understand how restaked assets can keep moving through DeFi.
This learning path makes it easier to build a complete picture than chasing some high-APY restaking product directly.
FAQ
Does restaking mean staking the same ETH twice?
From an economic security standpoint, it means letting already-staked capital take on additional security responsibilities, but it is not simply depositing the same ETH into two ordinary staking pools. The key to restaking is using already-staked capital to secure additional AVSs.
Is EigenLayer a new blockchain?
No. EigenLayer is a restaking protocol built on Ethereum, and its core role is to connect stakers, operators, and AVSs so that already-staked ETH can provide shared security to other services.
Are restaking returns always higher than staking returns?
Not necessarily. Restaking may offer extra rewards, but returns depend on the specific AVSs, incentive mechanisms, token prices, fees, and market conditions, and the extra rewards come with extra risk.
What is the difference between an LRT and an LST?
An LST usually represents a liquid staking asset tied mainly to base staking, while an LRT usually represents an asset that has gone through restaking. An LRT has more potential sources of return, but its chain of risk is also more complex.
What is the biggest risk of restaking?
The main things to watch are extra penalties and compounding risk, including slashing, smart contracts, operators, AVSs, liquidity, and the chain reactions that shared security can produce.
Is restaking suitable for beginners?
If you do not yet understand staking, LSTs, validators, and slashing, it is not advisable to start with complex restaking strategies. Understanding the basics of staking first makes it easier to judge risk when you later look into restaking.
Summary
The core of restaking is not "making one ETH earn two risk-free yields," but rather:
Letting the economic security already used for Ethereum staking be used again by other decentralized services.
The shared security model that EigenLayer represents lets AVSs build economic security using existing ETH staking capital, while stakers and operators can earn corresponding rewards by providing extra security services.
This model improves how efficiently staked capital is used, and it also solves part of the cold-start problem new services face when building a security system.
At the same time, however, the more security responsibilities an asset carries, the more complex its risks become.
So when judging a restaking project, do not look only at APY; check these in order:
Underlying asset → AVS → operator → source of yield → slashing conditions → exit mechanism → portfolio risk.
Only after you truly understand this chain can you judge whether restaking is improving capital efficiency or trading more complex risk for a higher potential return.
Crypto, staking, and restaking all carry relatively high risk. Restaking may involve smart contracts, slashing, operators, AVSs, liquidity, and systemic risks; actual returns can vary widely, and in extreme cases it can lead to asset losses. This article is for informational and educational purposes only and does not constitute investment advice.
Recommended
View more
service hotcoin.com
producthotcoin.com
businesshotcoin.com
casecnhotcoin.com